Snapshot Difference - Take a snapshot of your computer and find changes in your drive and/or registry (Updated Oct 2026)
Description
Snapshot Difference shows exactly what changed on your computer between two moments — for example what a program's installer added to the Windows Registry and to a folder, what a settings change really did, or what was left behind after an uninstall. Take a snapshot, make the change, then compare: every registry key and value that was added, changed or removed, and every file that was added, changed or deleted in the folder you chose, is listed.
You can snapshot any of the main registry hives (HKEY_CURRENT_USER, HKEY_LOCAL_MACHINE, HKEY_USERS, HKEY_CURRENT_CONFIG) and a folder on any drive, including network drives. Registry snapshots are saved, so you can compare after a restart, and you can keep named baselines to compare against later. Common background noise (recent-file lists, usage counters and similar) is filtered out automatically, and you can add your own filters.
How to use
 1.
Under
Registry Hives, tick the hives to include (
All /
None select them quickly). HKEY_CURRENT_USER takes a few seconds; HKEY_LOCAL_MACHINE is much larger and takes about half a minute. Leave them all unticked to compare files only.
2. Under
File System, click
Browse... and choose a folder to watch, or leave it blank to compare the registry only. The folder snapshot lasts until you close the window.
3. Click
Take Snapshot and wait for it to finish. Then install, uninstall or change whatever you want to check.
4. Click
Compare Differences. The
Summary tab shows how many registry entries and files were added, modified or removed.
5. The
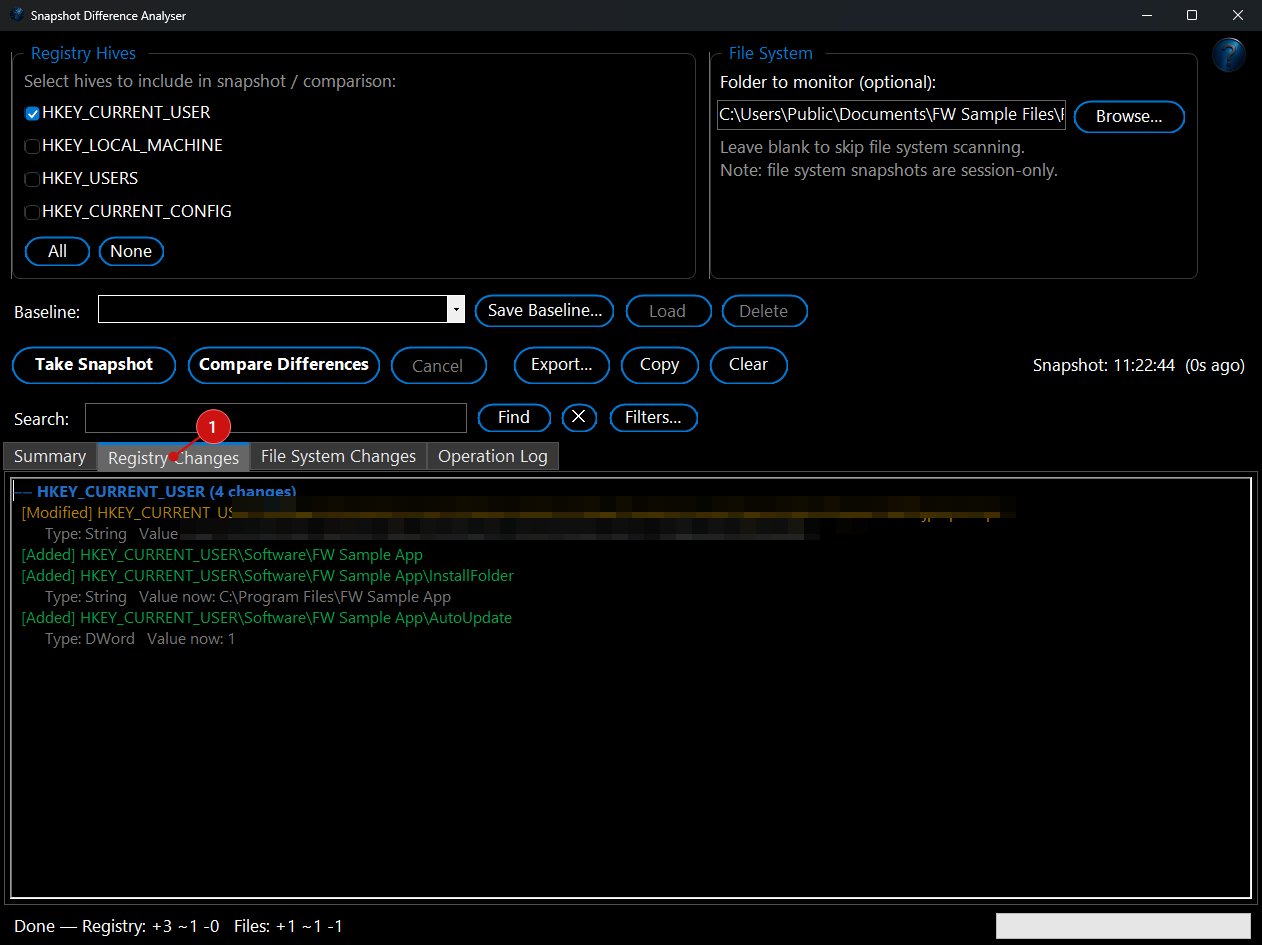
Registry Changes tab lists each key and value that changed, with its type and the value it has now.
 6.
The
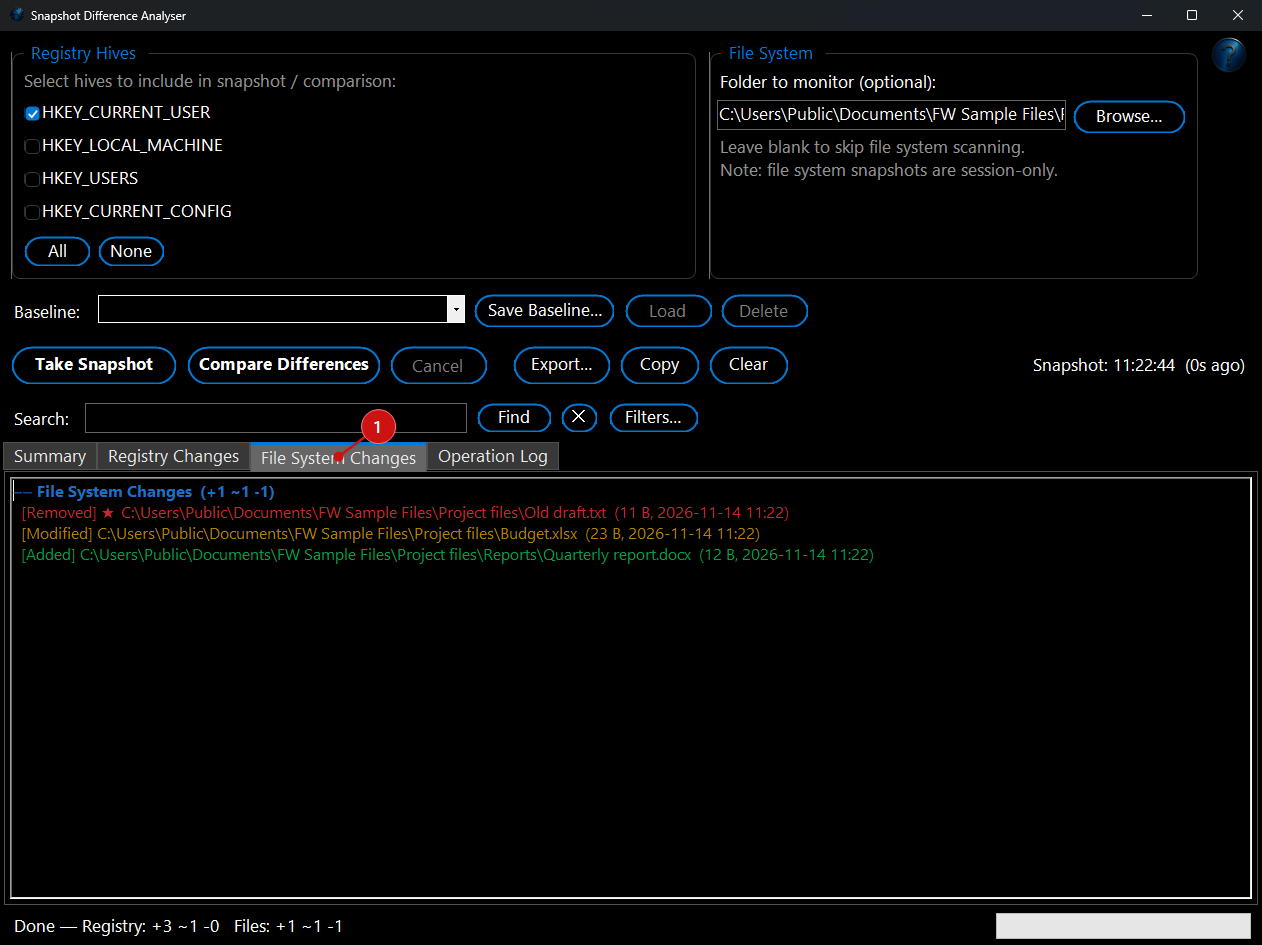
File System Changes tab lists each file that was added, modified or removed, with its size and date; important file types (scripts, settings, certificates and so on) are marked with a star. The
Operation Log tab records what was scanned. Use
Save Baseline... to keep the current snapshot under a name, and
Load or
Delete to use or remove a saved baseline.
 7.
Type in
Search and click
Find to find text in the current tab. Click
Filters... to add your own patterns for registry paths to ignore.
8. Click
Export... to save the results as a text or HTML file,
Copy to copy the current tab, or
Clear to start again.
Cancel stops a snapshot or comparison that is running.
Note: some parts of the registry can only be read by Windows itself; they are skipped and counted in the Operation Log.
What You Can Do With This Program
Potential Uses for Snapshot Difference Tool:
- Software Installation and Uninstallation Analysis:
- Identify exactly what files, folders, and registry entries a new software application adds or modifies during its installation. This is invaluable for understanding software behavior and potential conflicts.
- After uninstalling software, use the tool to find any leftover files or registry entries that the uninstaller missed, ensuring a complete and clean removal.
- System Troubleshooting and Debugging:
- Pinpoint changes to system files or registry settings that occurred just before a system started experiencing problems (e.g., crashes, performance degradation), helping to diagnose the root cause.
- Determine if a new driver, update, or configuration change introduced an unforeseen issue by comparing the system state before and after the change.
- Security Auditing and Malware Detection:
- Detect unauthorized changes to the operating system, installed applications, or critical system areas that could indicate malware infection, rootkit activity, or unauthorized tampering.
- By taking a baseline snapshot and regularly comparing, you can quickly spot suspicious new files, altered executables, or unexpected registry modifications.
- Configuration Management and Baseline Control:
- Document system configuration changes over time, creating a historical record for auditing purposes or to maintain known good baselines.
- Verify that planned configuration changes (e.g., applying security policies, changing network settings) have been successfully applied across systems.
- System Optimization and Cleanup:
- Identify temporary files, unnecessary registry entries, or residual data left behind by applications or system operations, aiding in deeper system cleanup and optimization.
- Forensic Analysis (Basic):
- In a controlled environment, this tool can provide an initial, quick overview of changes made to a potentially compromised system's file system and registry, aiding in basic forensic investigations. (Note: Professional forensic tools offer more in-depth capabilities).
- Development and Testing Environment Management:
- For developers and testers, track precisely what changes their applications make to the system during installation, execution, or uninstallation, ensuring predictable behavior and clean deployments.